I recommend taking your VPS off the public internet with Tailscale and Cloudflare Tunnel
Maybe important to repost this now that everyone is getting hacked
If you have a VPS, I recommend you to get if off the public internet and into a Tailscale network and Cloudflare Tunnel ASAP
It doesn't matter you have SSH key login, this is about exploits and vulnerabilities AI is finding
There's 2 ways into a VPS:
- via your site/app (like the PHP exploit of this week with a file upload hack)
- via your server (like hacking into SSH or some open port)
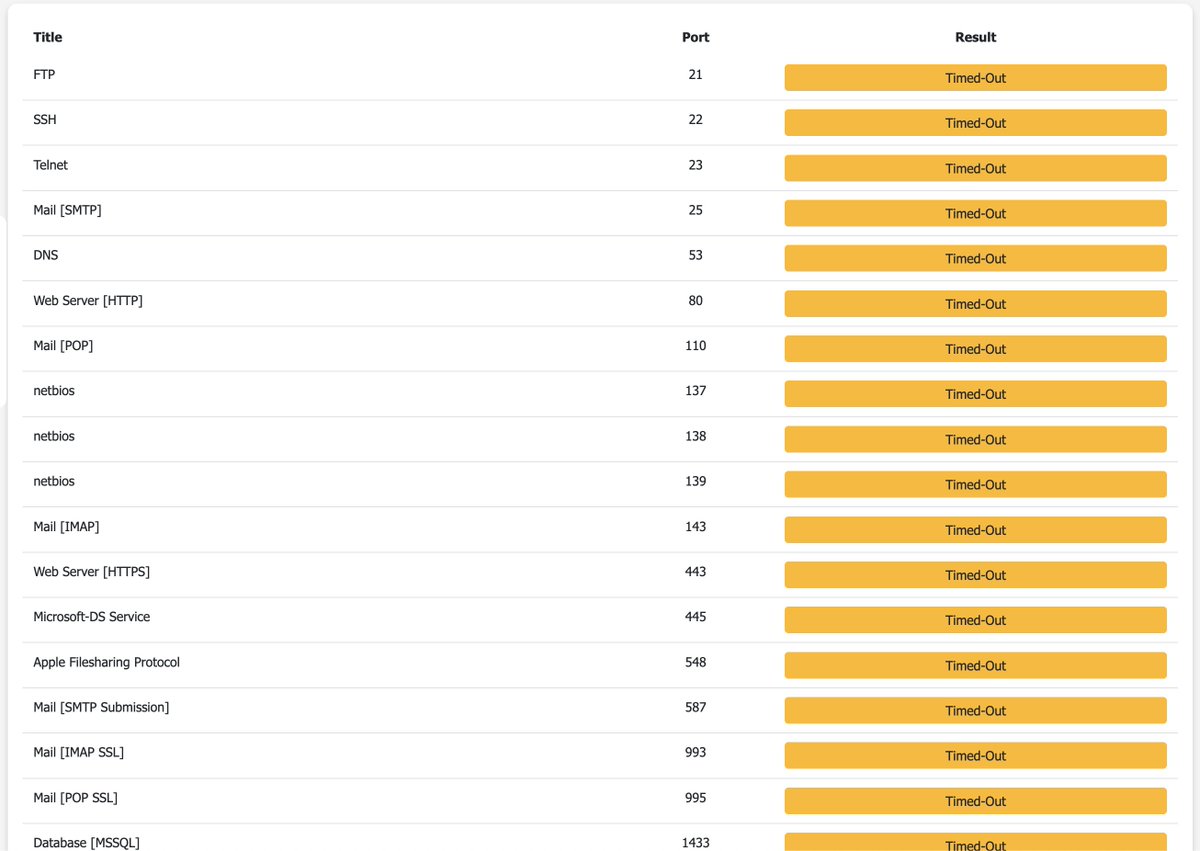
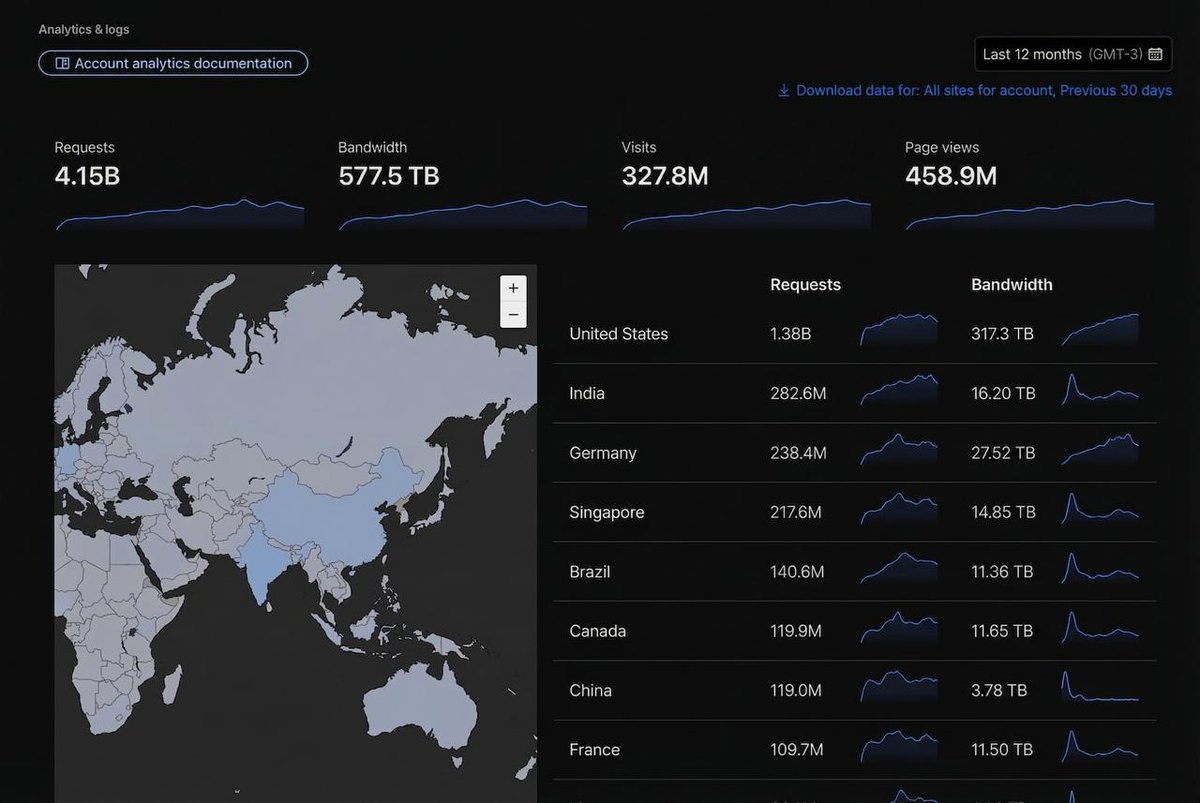
The site/app side you put on a Cloudflare Tunnel and then with the default Free Plan it has WAF security enabled by default and they jump on new security exploits fast, it means that the only way to reach your website is via the Cloudflare Tunnel, your server does not respond to port 80 or 443 anymore
The server side you put on a Tailscale network which is like your own private network that nobody can access but your own devices (like your laptop, your phone and your VPS) kinda like a VPN
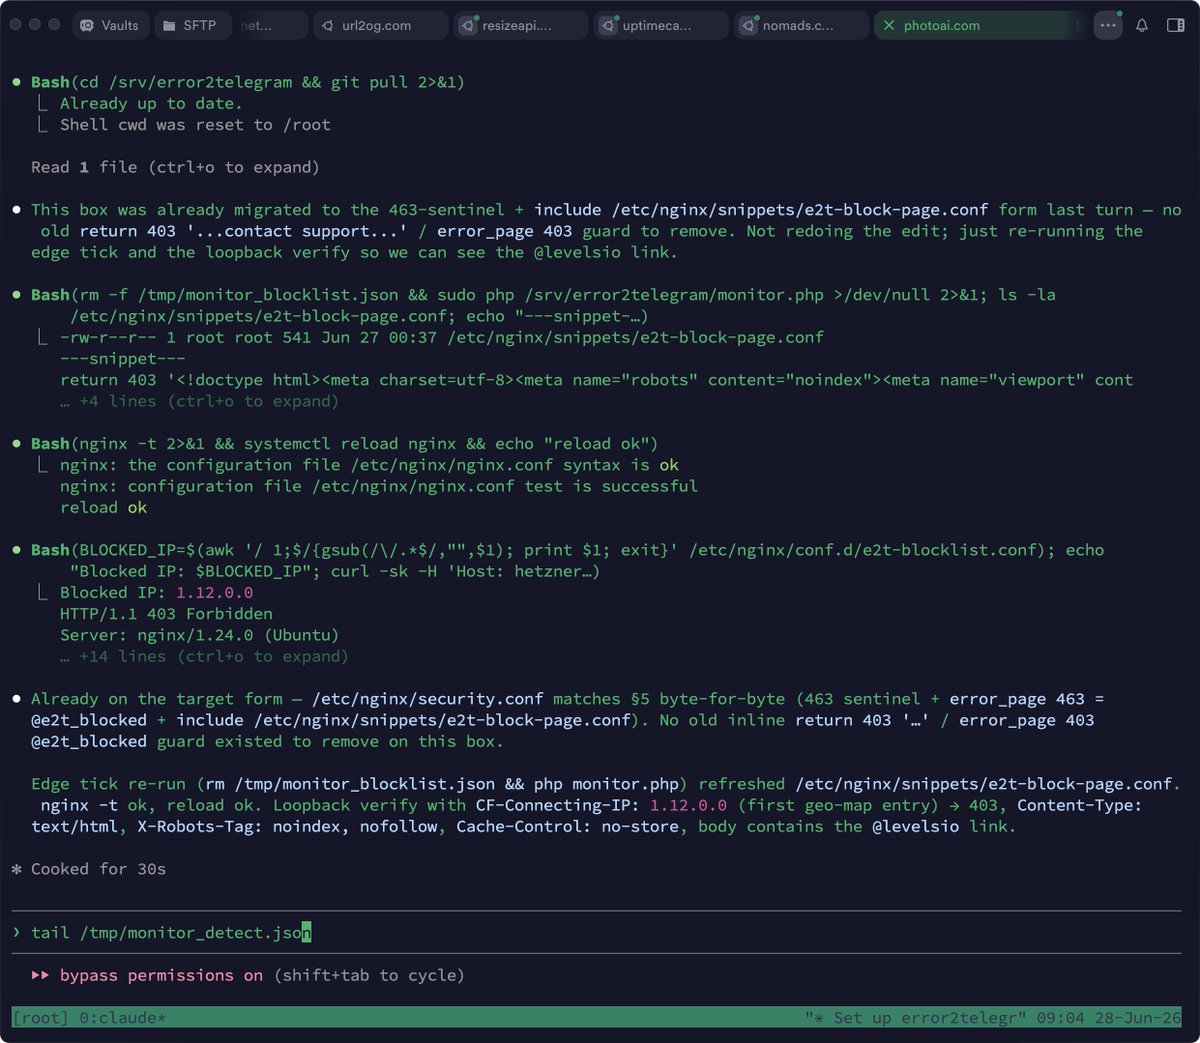
Then you switch off ANY regular access to your VPS on the firewall, in my case I use Hetzner and you create a new firewall then empty it and that blocks everything (test it)
How do Tailscale and Cloudflare Tunnel get in then? They don't. They go outbound. They make a tunnel to outside which sends and receives
Now you've reduced your attack vector to Tailscale and your Cloudflare Tunnel, much safer, not perfect btw, but nothing is
Originally posted on X · 💬 Reply to this on X
P.S. I'm on 𝕏 too if you'd like to follow more of my stories. And I wrote a book called MAKE about building startups without funding. See a list of my stories or contact me.
Never miss a post: 184,872 people read my posts in full by email, before it spreads anywhere else